The UK’s Cyber Security and Resilience Bill is moving through Parliament. It raises expectations around cyber resilience, incident reporting and supplier accountability. The direction of travel reaches far beyond IT and security teams.
Most companies do not think of themselves as technology businesses. Yet they now depend on cloud platforms, payment systems, CRMs, ecommerce tools, customer portals, logistics software and third-party APIs. That makes every company a connected company, whether it wants to be one or not.
Downtime means the tech that runs your business stops working. When it stops, revenue, customer experience and internal operations stop with it. Digital security is no longer only a defence against cyber attacks. It is a commercial, operational and board-level issue.
Resilience Is More Than Cybersecurity
Real resilience covers uptime, system monitoring, data access, backups, recovery plans, incident response and clear customer communications. It is a wide picture, and cyber attacks are only one part of it.
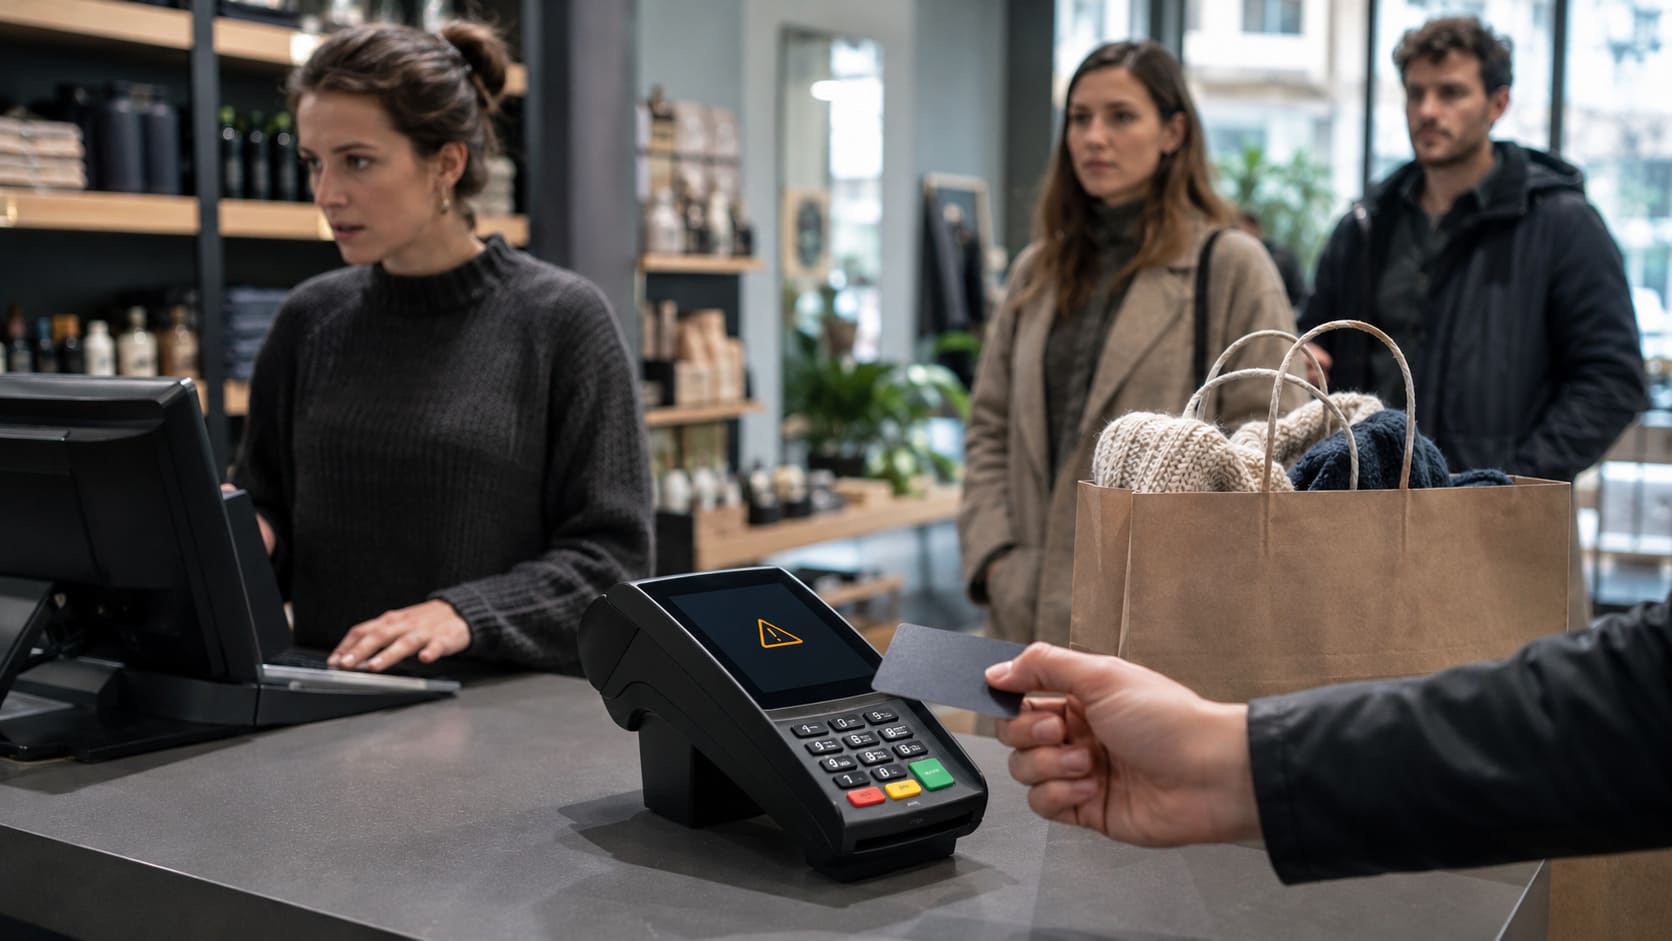
The real exposure is dependency. If one link in a connected system fails, the whole customer experience and revenue flow can break. A frozen payment gateway or an offline customer portal costs you sales the moment it happens.
Unplanned downtime is costly and common. Hardware failures, software errors and cyber incidents all trigger it, and research puts each minute of downtime at roughly $33,333. Even 99% uptime still means your systems sit offline for more than three days a year. Planning for failure is the smart move, not the pessimistic one.
The Supplier Problem
Many failures start outside the business.
They begin inside cloud providers, SaaS tools, payment platforms, agencies, MSPs, hosting partners and critical integrations. You feel the impact, but you do not always control the cause.
Real examples show how fast supplier failures cascade. The 2024 CrowdStrike outage grounded flights and froze payment systems worldwide, all from a single faulty update. The 2021 Fastly outage took Amazon, Reddit and the UK government website offline within minutes. The 2017 AWS S3 outage disrupted thousands of websites and services for hours, traced back to one mistyped command.
A single third-party dependency becomes a single point of failure you do not directly manage.
Supplier accountability is exactly what the new Bill sets out to strengthen.
What Businesses Should Do Now
Start by mapping your critical systems. Identify the single points of failure across your digital estate, from payment tools to hosting partners.
Review your supplier dependencies and know who holds the keys to each one. Document your recovery processes and test incident scenarios before a real one hits. Rehearsed teams recover faster, and speed is what protects revenue.
Modernise brittle integrations so one weak link cannot bring down the whole operation. Old, patched-together connections are often the first to break under pressure.
Treat digital security as a commercial opportunity. Companies that plan for failure avoid downtime, build customer trust, reduce operational drag and respond faster when things go wrong. That is a competitive strength, not just a cost.